外掛標籤
開發者團隊
原文外掛簡介
Securing a WordPress site often means juggling complex server configurations, confusing checklist articles, and heavyweight security plugins that slow down your admin or break production sites without warning. When managing multiple client sites, knowing which hardening steps have been properly implemented—and proving it to stakeholders—is even harder.
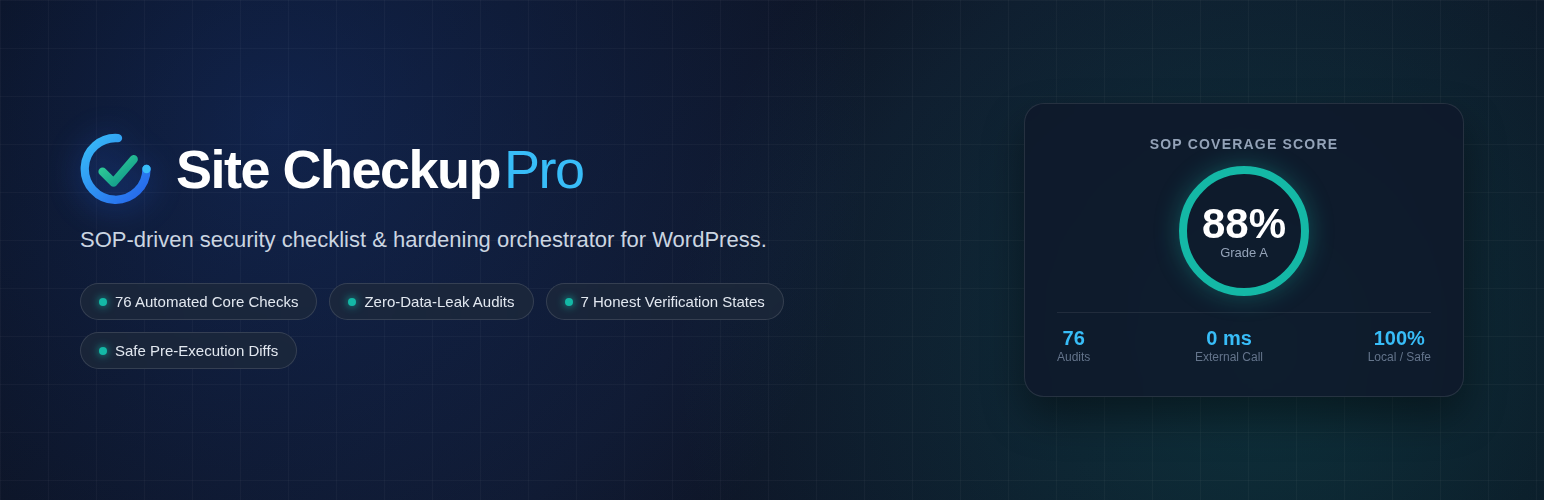
GeniousSonu Site Checkup solves this by giving you a clear, structured WordPress security hardening checklist paired with automated diagnostic scanners and safe, reversible fixes. Instead of guessing, you get an actionable SOP dashboard that audits your installation, previews every configuration change before applying it, and generates professional client-ready reports.
Rather than competing with or replacing mature firewalls and backup tools, GeniousSonu Site Checkup audits your environment, detects vulnerabilities, and applies verified, reversible hardening fixes with zero bloat. Automate safe security tasks, guide complex configurations with seamless plugin bridges, track routine credential rotations, and generate print-ready executive client audit reports:
Level A (Safe Automation & Scanners): Disable XML-RPC, restrict unauthenticated REST user enumeration, hide PHP versions, enforce clickjacking protection (X-Frame-Options), MIME sniffing protection, HSTS, disable front-end WP_DEBUG_DISPLAY, audit file permissions (strict 640 baseline on wp-config.php), detect risky PHP disable_functions / open_basedir, check default wp_ database prefix, external fingerprint scanner, and probe TLS protocols (TLSv1.0 through TLSv1.3) and certificate chain depth.
Level B (Guided Actions & Bridges): Seamlessly detects and bridges to mature, audited plugins (WPS Hide Login, Wordfence, Two-Factor Authentication, and Backup plugins) with recommended setting checklists. Generates RFC 9116 /.well-known/security.txt responsible disclosure contact files.
Level C (Manual Audits & Reminders): Track 15-day credential rotations (cPanel, WordPress admin), quarterly (90-day) backup restore test rehearsals, staging site HTTP basic authentication, and 6-month Google Search Console URL removal reviews with automated dashboard reminder notices.
Level D (Executive Client Reports): Generate print-ready HTML and PDF audit summaries detailing completed hardening, SOP coverage percentage, emergency incident-response escalation sheets, and timestamped audit logs for client handoff.
Built with Enterprise Safeguards
Vulnerability Intelligence: Queries the Patchstack vulnerability database API for installed plugins and themes with explicit confidence scoring (high, medium, unverified/low), ensuring custom or renamed plugins are never falsely reported as clean.
Server Environment Aware: Automatically detects Apache/LiteSpeed vs Nginx. If your site runs on Nginx, .htaccess tasks display copyable Nginx server directives rather than false positive checkmarks.
Zero Secret Leakage: Audit logs strictly redact passwords, auth keys, and database credentials. Constant changes log only boolean states; salt rotation logs zero key material.
Scoped REST API: Options updates are restricted to a hardcoded whitelist with strict per-field sanitizers, preventing mass-assignment vulnerabilities.
Pre-Execution Diff Previews: Inspect the exact marker-delimited configuration blocks before writing to .htaccess or wp-config.php.
Staging-Safe Health Checks: Automatic loopback tests detect staging HTTP Basic Auth walls and only roll back upon true 5xx server errors.
Safe Plugin Deletion: Unwanted migration tools are zipped to wp-content/uploads/genioussonu-site-checkup/plugins/ before deletion, making Undo 100% genuine.
Fail-Safe Emergency Lockout Recovery: Custom login renamer contains zero query-string backdoors. Recovery is exclusively controlled via the GENISICH_DISABLE_LOGIN_RENAME constant in wp-config.php.
Third Party Services
GeniousSonu Site Checkup connects to the following external third-party services to deliver security auditing and alerting functionality:
WordPress.org APIs (https://api.wordpress.org)
Service & Purpose: Used for core checksum validation (/core/checksums/1.0/) and verifying plugin directory status (/plugins/info/1.0/).
Data Sent: Current WordPress version, plugin slugs, and locale. No personally identifiable information (PII) or credentials are transmitted.
Privacy Policy: WordPress.org Privacy Policy
Patchstack Vulnerability Database API (https://patchstack.com)
Service & Purpose: Checks installed plugin and theme versions against the Patchstack vulnerability intelligence database to identify known CVEs.
Explicit Consent Required: Outbound queries to Patchstack require an explicit opt-in checkbox to be enabled in Plugin Settings per WordPress.org Guideline 7. If disabled, local plugin assessments are performed with zero outbound network calls.
Data Sent: Plugin and theme software slugs and version numbers. If configured by an administrator, an optional API authentication key is transmitted over HTTPS. No site visitor data, user credentials, or database contents are sent.
Privacy Policy: Patchstack Privacy Policy
Terms of Service: Patchstack Terms of Service
User-Configured Alert Webhooks (Optional)
Service & Purpose: When configured by an administrator, outbound security event notifications (e.g., brute-force lockouts, rogue admin detections) are dispatched to the customer’s chosen webhook endpoint (e.g., Slack, Discord, or agency automation endpoint).
Explicit Consent Required: Outbound alert dispatch requires an explicit opt-in checkbox to be enabled in Plugin Settings per WordPress.org Guideline 7.
Data Sent: Factual incident event summaries (timestamp, alert type, sanitized technical message). Audit logs and webhook payloads strictly redact passwords, security salts, and authentication tokens.
Terms & Privacy: Governed by the destination endpoint provider chosen by the site administrator.
GitHub Advisory Database (GHSA) (https://api.github.com)
Service & Purpose: Queries the GitHub Advisory Database GraphQL/REST API for known security advisories affecting installed WordPress plugins and themes.
Explicit Consent Required: Disabled by default. Outbound requests require enabling the GHSA toggle in Settings per WordPress.org Guideline 7.
Data Sent: Software component slugs and versions. If supplied, an encrypted GitHub Personal Access Token is sent in the Authorization header. No personal user data or site contents are sent.
Privacy Policy: GitHub Privacy Statement
Terms of Service: GitHub Terms of Service
Open Source Vulnerabilities (OSV) API (https://api.osv.dev)
Service & Purpose: Queries the Google OSV distributed vulnerability database for security advisories across open-source ecosystems.
Explicit Consent Required: Disabled by default. Outbound requests require enabling the OSV toggle in Settings per WordPress.org Guideline 7.
Data Sent: Software component names and version strings. No user or visitor personal data is transmitted.
Privacy Policy: Google Privacy Policy
Terms of Service: OSV Terms of Service
National Vulnerability Database (NVD) API (https://services.nvd.nist.gov)
Service & Purpose: Queries the NIST National Vulnerability Database for Common Vulnerabilities and Exposures (CVE) intelligence and CVSS scores.
Explicit Consent Required: Disabled by default. Outbound requests require enabling the NVD toggle in Settings per WordPress.org Guideline 7.
Data Sent: Software identifiers and version parameters. Optional encrypted NVD API key sent if configured. No personally identifiable information is sent.
Privacy Policy: NIST Privacy Policy
CISA Known Exploited Vulnerabilities Catalog (KEV) (https://www.cisa.gov)
Service & Purpose: Cross-references installed software with the CISA Known Exploited Vulnerabilities catalog to alert administrators of actively weaponized zero-days and exploits.
Explicit Consent Required: Disabled by default. Outbound requests require enabling the CISA KEV toggle in Settings per WordPress.org Guideline 7.
Data Sent: No site or user data is transmitted. Only a standard GET request to fetch the public catalog JSON feed.
Privacy Policy: CISA Privacy Policy
WPScan WordPress Vulnerability Database (https://wpscan.com)
Service & Purpose: Queries the WPScan vulnerability database for dedicated WordPress core, plugin, and theme security advisories.
Explicit Consent Required: Disabled by default. Outbound requests require enabling the WPScan toggle and providing an API key in Settings per WordPress.org Guideline 7.
Data Sent: Plugin and theme slugs and version numbers, along with the encrypted API token in request headers. No site content, visitor data, or user credentials are transmitted.
Data Handling Notice: In strict compliance with WPScan Terms of Service and data licensing, vulnerability intelligence data retrieved from WPScan is never permanently stored or cached on disk.
Privacy Policy: Automattic Privacy Policy
Terms of Service: WPScan Terms of Service
Source Code & Development
The full, unminified source code for GeniousSonu Site Checkup is developed publicly on GitHub:
https://github.com/GeniousSonu/Site-Checkup-Pro
All JavaScript and CSS distributed in this plugin are 100% human-readable, unminified, locally bundled, and licensed under the GNU General Public License v2 or later per WordPress.org Guidelines 2 and 4.
Credits
GeniousSonu Site Checkup is built and maintained by SK Sahinur Islam.
* Author Website: https://www.genioussonu.me/
* GitHub: https://github.com/GeniousSonu/
* WordPress.org Profile: https://profiles.wordpress.org/genioussonu/