外掛標籤
開發者團隊
原文外掛簡介
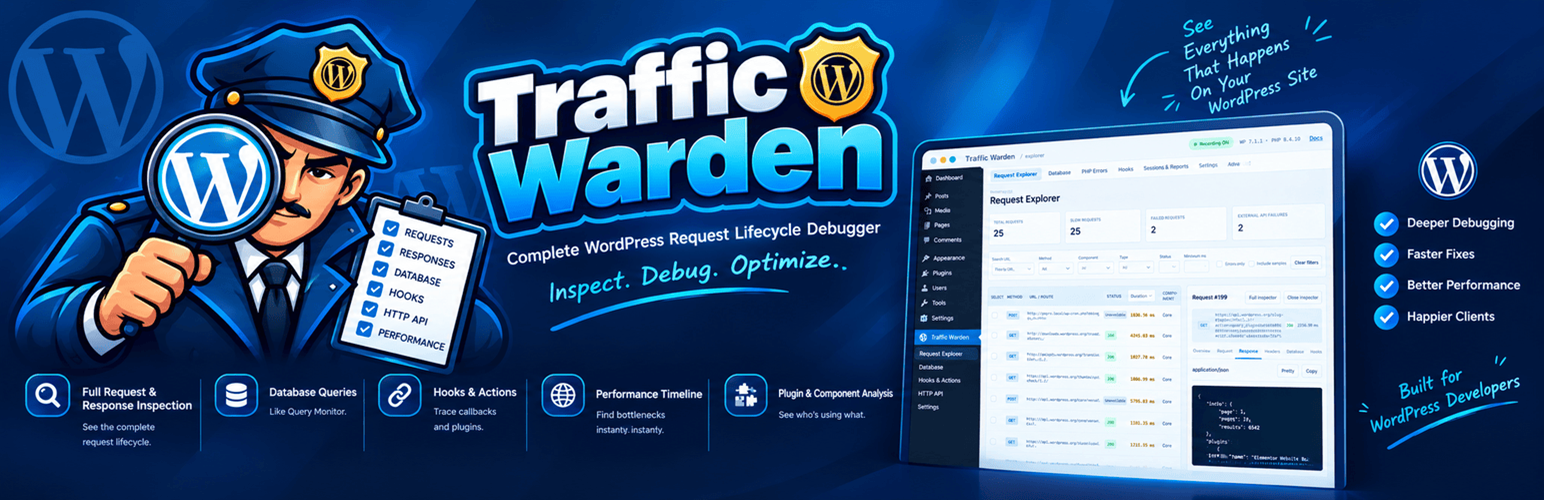
Traffic Warden provides a native administration dashboard for local diagnostics. Historical recording is disabled on activation; live inspection is enabled by default for authorized accounts. Administrators choose recording scope, retention, body capture and access permissions.
Features include searchable captures, incoming/outgoing correlation, caller attribution, sanitized JSON/form bodies, SQL timing and duplicate groups, shutdown fatal PHP errors, short-lived targeted capture, pagination and bounded cleanup.
Live Inspector adds an optional WordPress toolbar and lazy React dock with 17 current-request panels. Live inspection is enabled by default for authorized accounts on supported administration and frontend pages. Site and account settings can disable it; existing saved choices are preserved on upgrade. Live snapshots are private to the current account/session/site, expire after ten minutes and do not enable historical recording. Captured contents are not embedded in page markup or saved to browser storage. Admission and reads are bounded; delayed cleanup can delay physical removal after expiry. No second plugin or database drop-in is installed. Readable source is included; this readme describes activation and privacy.
Hook occurrence/registration inspection, a shared-origin timeline, sanitized JSON/HAR/SQL/body exports, POSIX cURL copying, CIDR/proxy rules, restricted redaction patterns, audit records, saved scopes, local sharing, comparison, component reports, regression review and permission-protected WP-CLI commands are included. Callback execution timings remain unavailable. HAR network phases are explicitly marked as projections. Saved scopes never bypass capture retention.
Advanced replay is disabled by default and limited to explicitly confirmed safe-method public HTTPS requests on staging with an exact hostname allowlist. Synthetic EXPLAIN is limited to a restricted read-only grammar and a MariaDB per-statement timeout adapter. No captured SQL is automatically executed and redacted credentials are never reconstructed.
Database timings require SAVEQUERIES to be explicitly enabled outside this plugin. Detailed database and stack collection requires WP_DEBUG when the production guard is enabled. Traffic Warden does not enable global query logging itself.
Capture starts after plugins load. Cached pages that bypass PHP, earlier bootstrap events and browser-side requests are outside coverage. General page output is not buffered; structured REST responses and WordPress HTTP API responses can be captured when body capture is enabled. Missing data is labelled explicitly.
Privacy: diagnostic data stays in this site’s database. No analytics or external service is contacted by the plugin. Bodies are off by default. Known credentials, SQL literals and common personal-data keys are removed before storage, but diagnostic content can still contain personal data. Restrict access and capture scope, and purge data after debugging. Retention defaults to seven days, 5,000 request rows and a 250 MB admission budget. WP-Cron performs bounded cleanup; delayed cron may delay physical removal. Deactivation stops collection. Uninstall retains data unless the administrator enabled deletion.
Author: Hammad Farooq Meer – https://hammadmeer.netlify.app
PHP diagnostics in 2.0.0 observe eligible fatal errors at shutdown after the collector starts. Nonfatal warnings, notices and deprecations are not intercepted. No error handler or reporting mask is installed or changed. A zero count does not prove absence of errors.