內容簡介
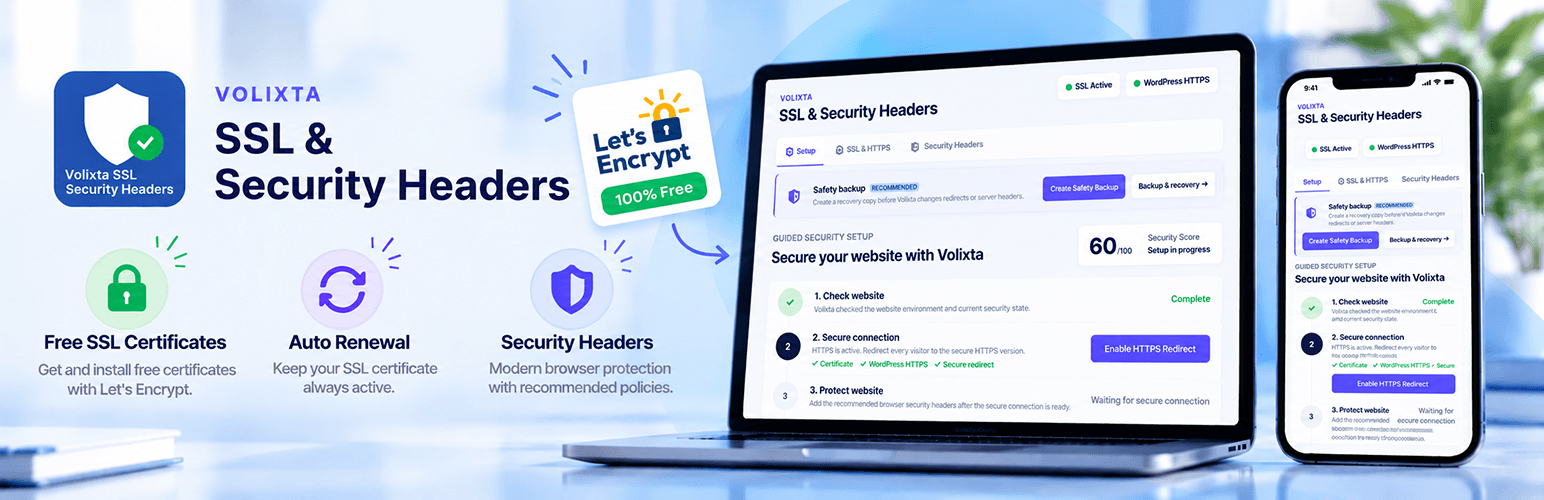
Volixta SSL & Security Headers 是一款幫助 WordPress 網站擁有者配置 HTTPS、管理 SSL 證書、修正混合內容並應用現代瀏覽器安全性的外掛,無需手動編輯敏感的伺服器檔案。
【主要功能】
• 引導式設置精靈,逐步指導 SSL 證書設置
• 免費 Let’s Encrypt SSL 證書請求與安裝
• 自動 SSL 安裝,支援 cPanel、Plesk 和 DirectAdmin
• 混合內容工具,包括前端檢查和即時修復
• 安全標頭設置,包括 HSTS 和 CSP
• 安全備份,確保 .htaccess 和 wp-config.php 的安全
外掛標籤
開發者團隊
② 後台搜尋「Volixta SSL & Security Headers」→ 直接安裝(推薦)
📦 歷史版本下載
原文外掛簡介
Volixta SSL & Security Headers helps WordPress site owners configure HTTPS, manage SSL certificates, fix mixed content, and apply modern browser security without manually editing sensitive server files.
Use Volixta to request free Let’s Encrypt certificates, install supported certificates through hosting integrations, switch WordPress to HTTPS, configure 301 redirects, and verify the certificate that visitors actually receive.
Key features include:
Guided Setup Wizard that checks your site first, then guides you step by step through SSL certificate setup, HTTPS activation, redirects, Security Headers, optional alerts, and a final status review.
Beginner-first Overview with advanced certificate, DNS, HSTS, CSP, Secure Cookies, Mixed Content, file, backup, and recovery tools available when needed.
Free SSL certificates with Let’s Encrypt ACME v2 using automatic HTTP-01 or manual DNS-01 validation, including wildcard certificates.
Automatic SSL installation for supported cPanel, Plesk, and DirectAdmin environments, with hosting account connection directly from the Setup Wizard and downloadable certificate files for manual installation.
Automatic renewal checks for eligible HTTP-01 Volixta-managed production certificates, with clear renewal status and guidance for manual DNS-01 certificates.
HTTPS setup and redirects with guarded Apache/LiteSpeed .htaccess changes and clear Nginx guidance.
Mixed Content tools including frontend checks, Deep Scan, Live Fixer, and serialization-safe database cleanup.
Security Headers including HSTS, CSP, CSP Report-Only, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP, and CORP.
Secure Cookies for WordPress authentication and PHP sessions with Secure, HttpOnly, and SameSite=Lax protection.
Safety Backups before managed .htaccess changes. wp-config.php backups are downloaded directly to your computer and are not stored by Volixta on the server.
Certificate and protection alerts for upcoming certificate expiry, recent renewal failures, and protection regressions.
HSTS preload assistant that verifies the public Strict-Transport-Security response before reporting preload readiness, without submitting your domain to an external preload service.
Hosting-aware guidance for Apache, LiteSpeed, Nginx, reverse proxies, Cloudflare, localhost, and manual certificate workflows.
Local development support with a simplified Setup Wizard that avoids unsupported production-only actions while keeping compatible local HTTPS workflows available.
Volixta is designed to fail safely: it uses marked configuration blocks, verifies backups and file snapshots, and avoids overwriting unrelated .htaccess content.
External Services
Volixta does not send telemetry or usage analytics. External connections happen only when an administrator explicitly uses a feature that requires them.
Let’s Encrypt / ISRG — used when you request or renew a certificate. The requested domain names and ACME protocol data are sent to Let’s Encrypt. The ACME contact email you provide is sent to ISRG with the account request. See https://letsencrypt.org/repository/ and https://letsencrypt.org/privacy/.
Hosting control panels — cPanel, Plesk, or DirectAdmin are contacted only after you explicitly configure the integration and request certificate installation. Certificate/private-key material is sent only to the hosting endpoint you configured or that Volixta safely detected.
Your own public website/DNS — certificate, HTTP-01, DNS-01, HTTPS, header, and Mixed Content checks may connect to the site/domain you are administering. These checks do not send data to Volixta.
Privacy
Volixta SSL & Security Headers does not include analytics, usage tracking, or visitor tracking.
The plugin stores the configuration required for enabled features inside your WordPress installation.
Some actions communicate with external services when you explicitly use features that require them.
Examples include:
Let’s Encrypt: certificate requests and ACME validation.
Hosting integrations: configured cPanel, Plesk, or DirectAdmin connections used for certificate installation.
Only information required to perform the requested operation is sent to those services.
Localization
Text domain: volixta-ssl-security-headers
Load path: /languages
What’s Next
If you like this plugin, check out our other tools:
VOLIXTA Booking – The All-in-One WordPress Booking Plugin
Manage unlimited staff, services, clients, payments, and locations in one powerful system.
Volixta Analytics Lite – Privacy-first WordPress analytics with real-time visitors, traffic insights, and essential website statistics.