外掛標籤
開發者團隊
② 後台搜尋「ScanForge File & Theme Security」→ 直接安裝(推薦)
原文外掛簡介
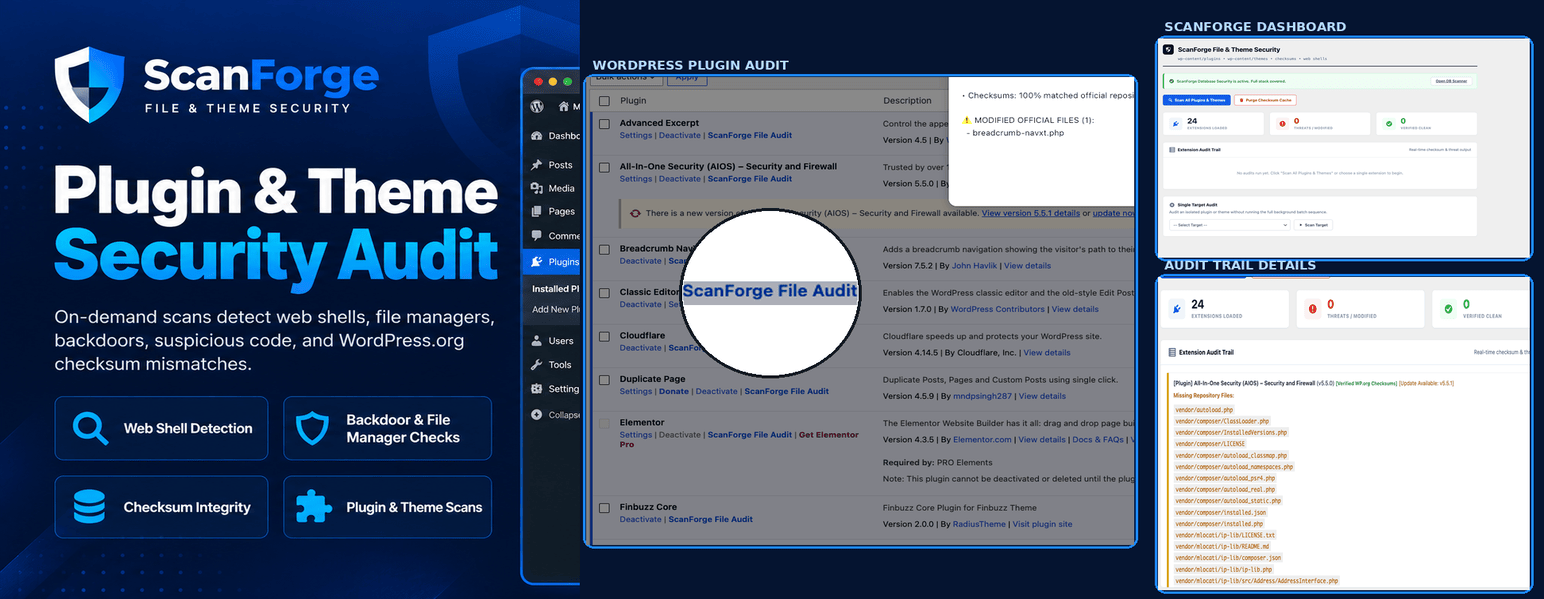
ScanForge File & Theme Security is a dedicated static code analysis and file integrity scanner built to detect unauthorized code modifications, web shells, and hidden backdoors across WordPress plugins and themes.
Unlike heavy, background-daemon security suites, ScanForge is an on-demand auditing engine. It gives system administrators and developers instant visibility into file tampering by comparing local plugin code against official WordPress.org release checksums while heuristically hunting for malicious payloads.
How ScanForge Protects WordPress Files & Themes
Official WordPress.org Checksum Verification: Instantly identifies modified repository files, unauthorized rogue additions, or missing script components by comparing local hashes directly with official release manifests.
Web Shell & PHP Backdoor Detection: Heuristically matches file contents against known malicious signatures, including WSO, b374k, FilesMan, c99, and r57 web shells.
Injected File Manager Discovery: Detects unauthorized dropped file management utilities (such as Tiny File Manager variants) via distinctive functional signatures (FM_ROOTPATH, FM_SESSION_KEY).
High-Risk Code Pattern Flags: Uncovers dangerous execution wrappers such as nested eval(base64_decode()), dynamic assertion backdoors, and shell execution handling raw superglobal inputs ($_POST, $_GET, $_COOKIE).
Intelligent Vendor Whitelisting: Automatically ignores standard dependency trees (vendor/, node_modules/, tests/) to eliminate false alarms and maximize scanning speed.
On-Demand & Lightweight: Runs sequential, memory-safe audits only when you click “Scan”, leaving zero background cron overhead on your server.
Full-Stack Security Integration: Seamlessly pairs with ScanForge Database Security to audit SQL tables (wp_posts, wp_options) alongside your filesystem scripts.
External Services & Privacy
This plugin queries official WordPress.org endpoints to verify plugin file integrity and check for available updates.
Service Used: WordPress.org Checksums and Plugin Information API (api.wordpress.org / downloads.wordpress.org).
Purpose: Retrieves official release MD5 hashes and plugin metadata to identify modified, added, or outdated files.
Data Transmitted: The plugin slug and installed version number are transmitted via standard HTTP GET queries. No personal data, visitor information, site contents, or admin credentials are transmitted.
Privacy Policy: All interactions with WordPress.org servers are governed by the WordPress Foundation Privacy Policy: https://wordpress.org/about/privacy/